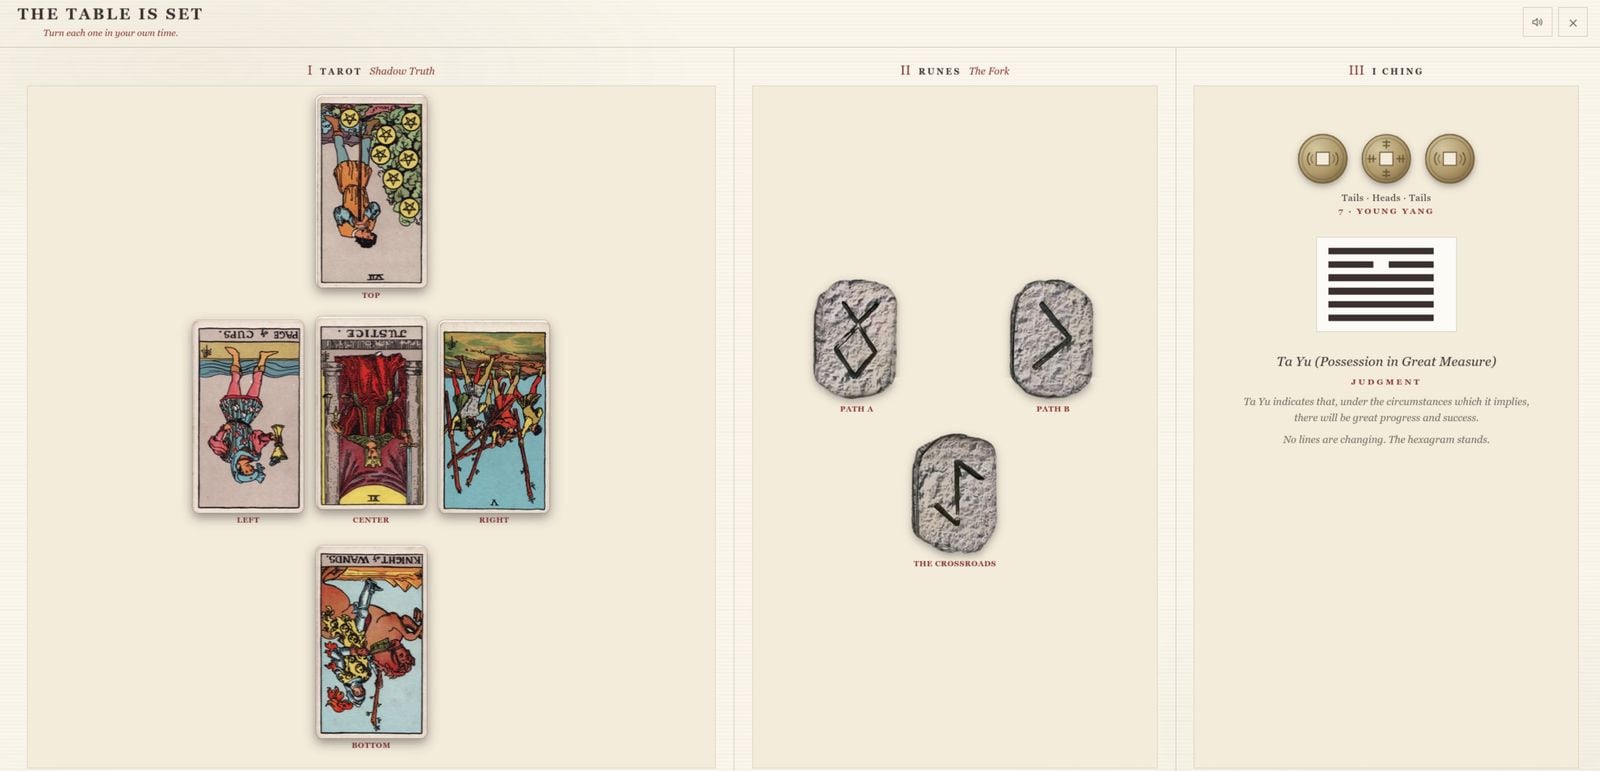
AI · Holy Oracle
Unlocking Ancient Wisdom with AI
Archetypal symbol analysis and historical divination
// AI engineering
We help companies put language models and coding agents to work safely: sandboxed, self-hosted where it matters, and tested against how they fail, not only how they demo.
// What we offer
AI coding agents running in hardened, rootless containers, with a written threat model, a verification run on your machines and clear rules for review and production access. Based on our open-source agent-pod project.
Open-weight models served with vLLM or llama.cpp on your own or in-country infrastructure, monitored, and with documented failure behaviour, for data that should stay under your control.
We measure how your model or agent setup behaves when things go wrong: timeouts, lost nodes, recovery cost and gaps in isolation. You get measured findings, not a checklist.
Summaries, extraction, classification and assistants built on the major model APIs, added to the web and mobile apps you already run.
A short experiment with success criteria agreed before we start, and a straight go or no-go at the end. A negative result is still a useful result.
// Research
Our AI work is backed by open experiments with predictions written before measuring, and results reported even when they are negative.
Persistence is an asymmetry problem: the defender has to find everything, while the attacker only has to leave one thing behind.
AI · Holy Oracle
Archetypal symbol analysis and historical divination
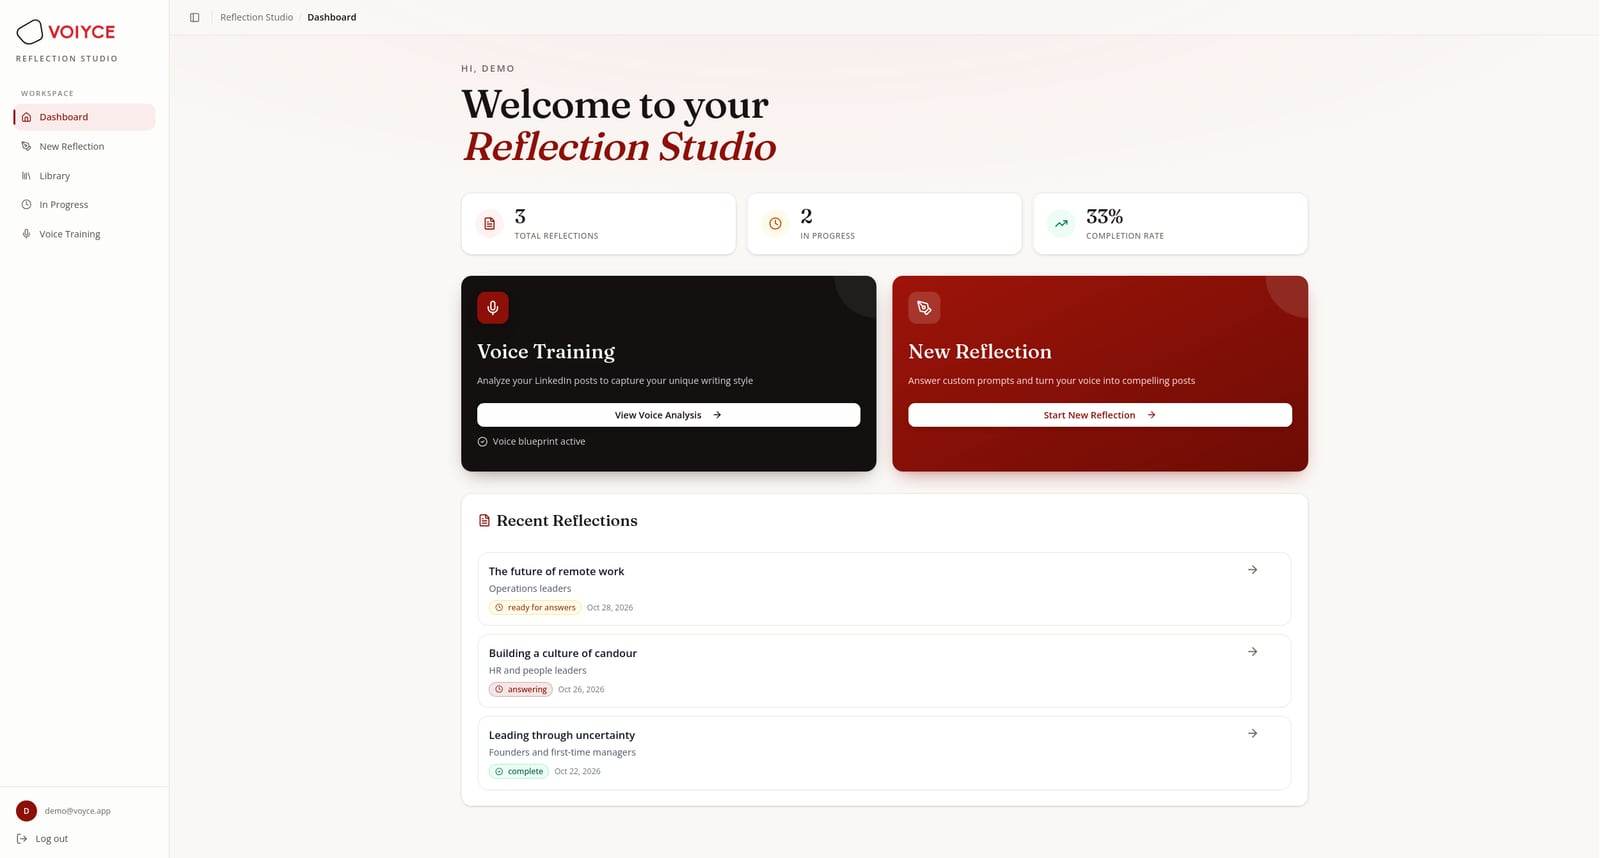
AI · VOIYCE
Automating professional social media strategy
Platforms and systems · RizqX
RizqX came to us with a web platform built in Plasmic that they wanted to keep. We integrated with it, took over their development and release pipeline, built their Flutter app for iOS and Android, and a year later moved them off Plasmic altogether.
// Questions
We configure providers' business and zero-retention options where they exist. When data cannot leave your infrastructure at all, we host the model for you instead.
With a call about the problem you want AI to solve. If a proof of concept makes sense, we scope it in writing, including what success looks like, before any work begins.
It can be, with isolation, review and limited access. That is exactly what our agent setups are built around: the agent never gets production credentials and every change is reviewed by a person.
// Next step
Book a free 30-minute call. We'll tell you plainly whether we're the right fit, and if we're not, who might be.